Six recommended security measures for corporate websites using WordPress

Hello, I'm Sato from non-standard world.
WordPress, introduced as a standard in corporate site CMS (update system), is an essential tool given the convenience of operation but it should be remembered that there are always security risks.
However, there may be some people who are concerned about what specific measures will be needed.
Today, we will introduce the recommended security measures to corporate sites that have introduced WordPress.
Contents [ hidden display ]
Protection of WordPress Management Screen
This is a countermeasure against attacks that attempt to hit the management screen and guess user name/password.
Countermeasure 1-1: Access Limitation by IP Address
By limiting access to the management screen by IP address, you can only access it from a specific place (company).
Specifically, we will apply IP restriction to the following.
- /wp-login.php
- /wp-admin/ * Excluding admin-ajax.php
Measures 1-2: Two-step authentication (recommended)
In addition to authenticating with a normal username and password, it also provides a more secure environment by authenticating using your smartphone, making it convenient for you to use Google’s two-step authentication system that uses your phone.
Countermeasures 1: Login lockdown (recommended)
If the user name and password have been entered incorrectly, there is a possibility of total attack, so access from that IP address will be locked out for a certain time.
Countermeasure 1-4: Leave logs of access and operations (recommended)
It is possible to monitor suspicious operation by leaving the operation history in case it was taken over.
Protection of Database Information
This is a measure about an attack that tries to steal "database connection information" of WordPress.
Countermeasures 2-1: Limitation of access to wp-config.php (recommended)
php with database connection information is prohibited from external access.
Countermeasures against Falsification of Corporate Website
It is a countermeasure against attacks that attempt to exploit malware (malware) and tamper with the contents of corporate sites by exploiting program vulnerabilities.
Measures 3-1: Limitation of access to wp-includes
Make sure that the folder below wp-includes which contains a core function of WordPress is not accessible from outside.
Countermeasures 3-2: Disable file editing (recommended)
You can not edit WordPress theme files (design information) and plugin files (additional functions) from the WordPress management screen.
Countermeasures4. Introducing security measures plugin
This is a comprehensive measure against various attacks on corporate sites.
Measures 4-1: Introducing iThemes Security, a comprehensive security plugin (recommended)
security plugin that detects and countermeasures various attacks iThemes Security We will introduce.
Countermeasures 4-2: Introduction of Theme, Plugin Checker (Recommended)
Introducing a plugin to check if there is any vulnerability in the theme, plug-in.
Introduction of automatic backup
In the unlikely event that a corporate site is falsified or cracked, it will be required for smooth recovery.
Countermeasures 5-1: Introduction of VaultPress, an antivirus and automatic backup service
This Web Service Lets You Regularly Check and Back Up Your Virus VaultPress In addition to preventing virus infection, recovery work in case of infection can be carried out smoothly by introducing “recovery process”.
* We need to make sure that backing up data to external services is not a problem with security policies.
Measures 6. Introduction of Firewall
It prevents malicious access from reaching the web server.
Countermeasures 6-1: Introducing CloudFlare Firewall Service
a service that speeds up the site and provides firewalls (the ability to prevent malicious access from reaching web servers) CloudFlare By introducing the “Accidental Attack”, it prevents attacks at waterfront.
* It is not necessary to install a firewall on the current server.
How was it? If you have installed WordPress but haven't taken measures, we recommend that you implement the measures as soon as possible.
We hope you will realize a safe CMS environment and operate our corporate website.
「 Solving the troubles of corporate site personnel! In the “Contact Us” section, we are looking for questions and questions that corporate web personnel have on a regular basis.
For those who have introduced questions on our blog, we will present you with an original postcard set.
Please feel free to contact us for any small questions from the following “Commentary Sending Form”.
*When posting a blog, please be assured that the company name or your name will not be published.
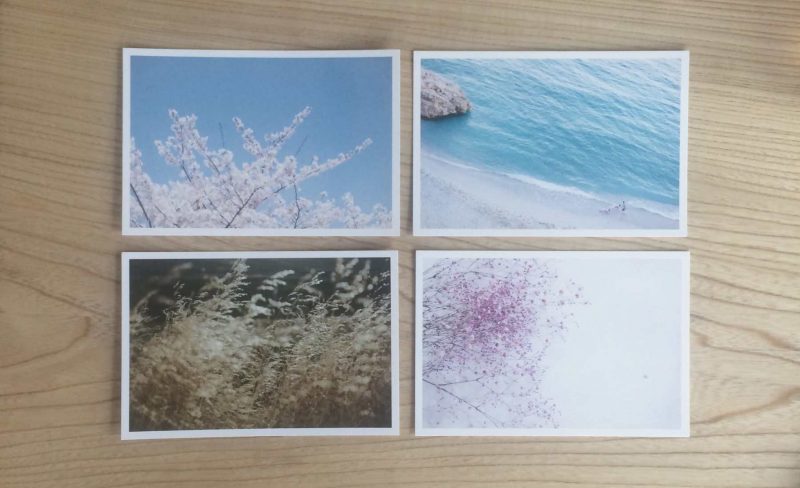
postcard set image
Pictures and contents may change.